RandomlyOpenCD.VBS

I got a call from a friend who was sure his PC was hacked because his CD-ROM drive kept randomly opening and closing.  After looking at the machine I found a .vbs file in his appdata folder named RandomlyOpenCD.VBS (surprisingly It randomly opens and closes the CD drive) and nothing else that looked like an APT.

After making a copy of the code, deleting the file and rebooting his PC it was fine and his CD drive was back to a non-hacked state. 

The practical joker in me makes it nearly impossible to not share the code:

Dim smax, smin, rmax, rmin, start, repeat
smax=900000
smin=300000
rmax=600000
rmin=100

Set oWMP = CreateObject(“WMPlayer.OCX.7”)
Set colCDROMs = oWMP.cdromCollection

Randomize
start=(Int((smax-smin+1)*Rnd+smin))
wscript.sleep start

do

if colCDROMs.Count >= 1 then
For i = 0 to colCDROMs.Count – 1
colCDROMS.Item(i).Eject
Next
For i = 0 to colCDROMs.Count – 1
colCDROMs.Item(i).Eject
Next
End If

Randomize
repeat=(Int((rmax-rmin+1)*Rnd+rmin))
wscript.sleep repeat

loop

Saying No

Last night I sent an email to a good friend and his boss passing on an amazing career opportunity that paid an ungodly amount of money.

It was basically Scrooge McDuck build a money bin money.

So why didn’t I take it?  After a lot of thinking and discussion with my wife it boiled down to timing and location.

We weren’t crazy about the location. We would have had to relocate to Atlanta. We dont have more than a handful of friends in Atlanta and our nearest relatives would be about 300 miles away.  I dont like grits.

The timing wasn’t great either. My son is getting ready to start Kindergarten next month. My wife has a job that she loves. Our family is a half hour drive away.  We have amazing friends. We love our church. I dont like grits.

Even after that list of cons It was still amazingly hard to say no to a great career opportunity and the possibility of my own money bin.

So why did I?

I remember seeing this quote a few months ago:

“Half of the troubles of this life can be traced to saying yes too quickly and not saying no enough.” – Josh Billings

So I took my time and thought about it.  On Monday I was ready to call a Realtor and put my house and the market. On Tuesday I was trying to figure out if I was going to sound cool with a southern accent.  On Wednesday I woke up and realized it wasn’t the right time to move our family half way across the country.

So yesterday I wrote an email apologizing and declining the position, put in a 16 hour day at my current job and went home and slept like a baby.

It will be hard not owning a Tesla and having a bin full of money to swim around in but I know I made the right choice for my family and hopefully there will be other opportunities like this in the future. 

Text Bombed

image

This afternoon a “hacker” decided to text bomb my phone with about 1000 text messages asking me to paypal him $100 to stop.

A couple of things:

  1. I don’t negotiate with terrorists. (I always wanted to say that.). 
  2. Part of the text bomb gave me information on how it was happening.

After getting a couple of messages I noticed they were all coming from onlinetextmessage.com.  After looking at their web page I noticed that you could block messages from their site to your phone.

Once I blocked the attack I was interested in how they did it and started to do a little bit of research. 

I am about to give you a link to a script that can do bad things. Please dont do bad things.

With a few well placed Google searches (onlinetextmessage.com sms bomb) I found this pastebin with a two year old perl script in it. I am “researching” here so I had to test out the script myself (against my own phone) and surprisingly it works really well. 

After looking at a couple of other online SMS sending website it appears the reason that onlinetextmessage.com is vulnerable to this abuse is because they dont ask for a capatcha before sending the message.  This would seem to be a pretty easy addition to their code to stop this from happening.  I have sent them a nice email asking this to make these changes. I doubt I ever hear from them.

Why I Hate My Alarm Clock

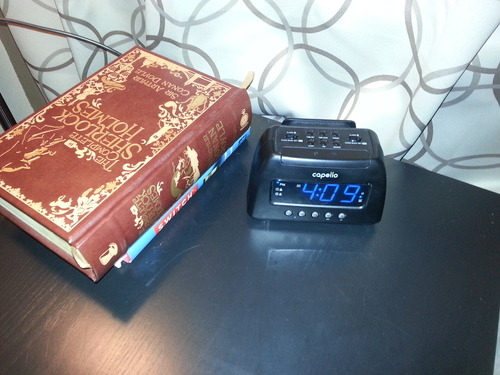
Meet the Capello Sleep & Charge Dual Alarm Clock with Night Light sold exclusively by Target.

It works fairly adequate as a:

  • USB Charging Station
  • Alarm Clock
  • Radio
  • Night Light(?)

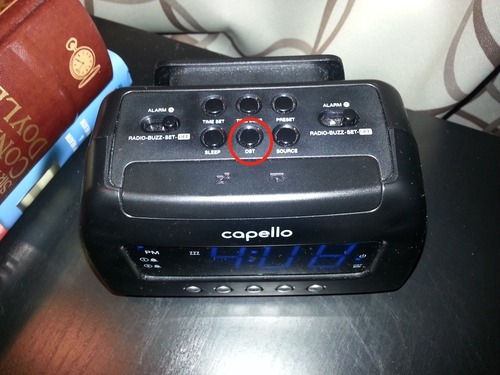
Why I hate it is this button right here:

This “DST” button is .25" away from the snooze button, .2" away from the source and sleep timer button. 

Why is this a big deal? Because when you accidentally touch the button it magically makes it an hour earlier in my bedroom than in the rest of the world.  For a feature that will save me 30 seconds two times a year they have basically put a self destruct button right on top of their product.

How in the world do products like this make it to the market?

The Most Difficult Question In Security.

I was having a conversation about security today with a good friend and the subject came up of what is the most difficult question in security to answer?

After a few minutes of back and we fourth we settled on the following question: 

Who would want to hack us?

This question is nearly always asked with the person asking it implying they aren’t important enough to be hacked.  

As security professionals we mostly do a terrible job at answering this question. Normally we end up answering with something vague like “hackers”.

image(This is what a hacker looks like.)

When we answer back with a vague answer like “hackers” we dont make the threat real to the person asking the question.  They will care and think about hackers as much as they do the nebulous bad guy who might break into their car and steal their 3 Doors Down CD.

The best way I have found to answer this question is by asking a question back. 

Here are a few questions I always try to ask back when someone asks me who would want to hack us?

Have you ever had an employee leave on bad terms?
Have you ever made a competitor mad?
Is there anyone that would enjoy you having negative publicity?

Everyone can think of an answer to one of these questions and it plants a mental image of someone who would actually want to do their company harm and not a guy with a ski mask.

How do you answer the question: Who would want to hack us?